Deepfake fraud has crossed an important threshold. It is no longer only a reputational, misinformation or consumer-scam problem. It is now a material enterprise financial risk.
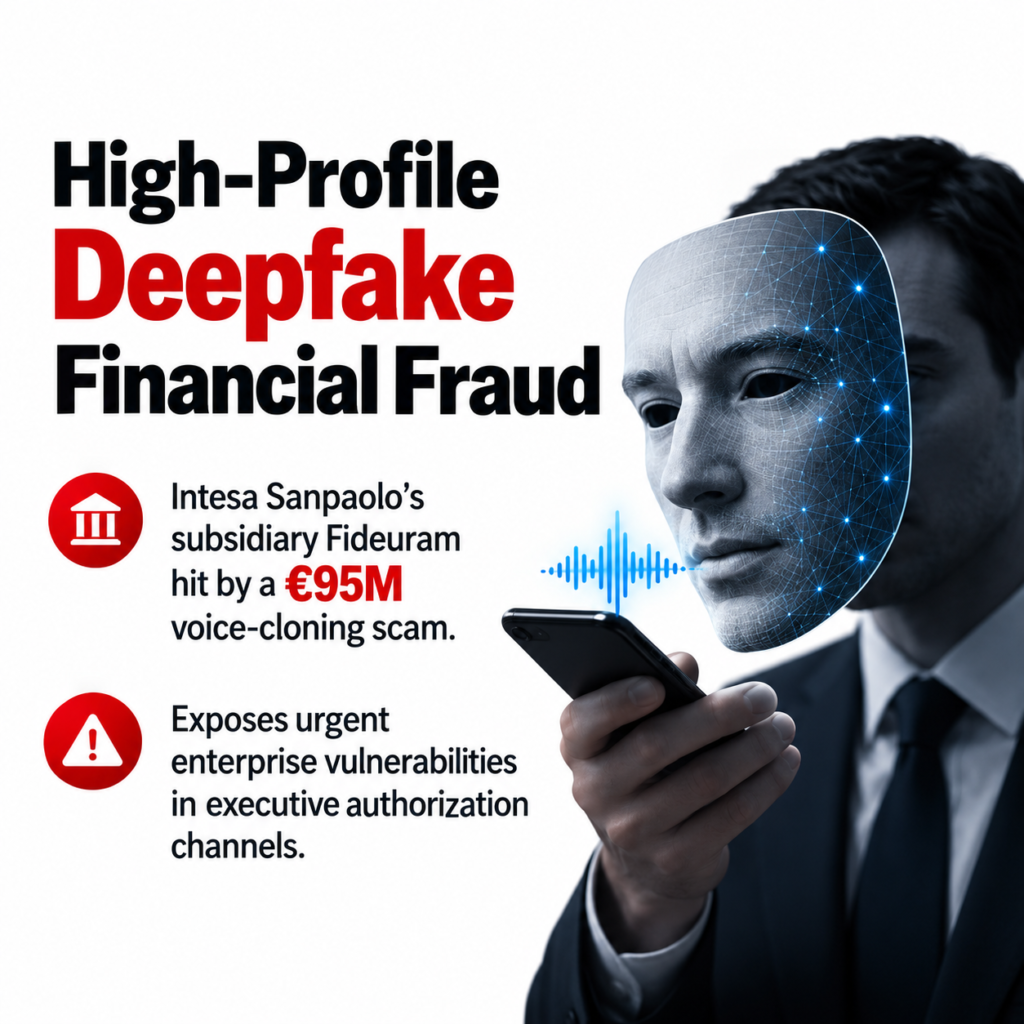
In February 2026, fraudsters reportedly targeted Fideuram, the private banking subsidiary of Intesa Sanpaolo, with a layered executive-impersonation scheme. According to Reuters and Trending Topics, the then-chairman of Fideuram received a WhatsApp message appearing to come from Intesa Sanpaolo CEO Carlo Messina. A later phone call used an AI-cloned voice of a senior lawyer known to the target, reinforcing the legitimacy of the request.
A series of overseas transfers totaling approximately €95 million followed, mainly to accounts in China and Hong Kong. Around €53 million was later recovered, while roughly €36 million remained unaccounted for in the reporting.
For enterprise security leaders, the key lesson is not simply that voice cloning works. It is that authorization architecture can fail when identity is inferred from familiar communication rather than independently verified.
The Attack Targeted Process, Not Just Technology
The scheme reportedly combined messaging, voice and email to construct a believable sequence.
This is significant because many organizations still treat channel diversity as verification. A request received by message may be “confirmed” over a phone call, while payment details arrive through email. That feels like three points of evidence.
It may actually be one attacker controlling three channels.
Traditional anti-fraud controls were designed around forged emails, compromised accounts and suspicious bank instructions. Generative AI strengthens social engineering by reproducing characteristics that people instinctively trust: a familiar voice, executive language and a plausible sense of urgency.
The control objective therefore has to move from “Does this sound authentic?” to “Was this request verified independently?”
Executive Authorization Is a Privileged Function
Cybersecurity teams understand privileged access in IT. Administrator accounts receive additional controls because they can make high-impact changes.
Financial authority deserves the same treatment.
Executives, treasury leaders and senior finance staff can initiate or authorize transactions with material consequences. Their authority should therefore be protected with predefined workflows that cannot be bypassed merely because a request appears urgent or confidential.
High-value or unusual payments should require maker-checker controls, separation of duties and independent approval. Changes to beneficiary information should trigger additional validation. Verification should use contact details and channels established before the transaction, rather than information delivered by the requester.
For particularly sensitive payments, organizations can define thresholds that require escalation to a second executive, treasury committee or designated risk function.
Deepfake Resilience Requires Cross-Functional Ownership
This is not only a finance problem and not only a cybersecurity problem.
Finance understands transaction workflows. Cybersecurity understands identity, social engineering and monitoring. Risk teams understand control design. Internal audit can test whether safeguards work in practice. Legal and communications teams may also be needed when impersonation involves external parties.
Organizations should therefore incorporate deepfake-enabled fraud into tabletop exercises and business email compromise simulations.
Testing should answer practical questions.
Can an executive bypass normal approval because a deal is confidential? Can one individual create and release a high-value payment? How are new beneficiaries verified? What happens when a senior leader pressures staff to move quickly? Who can stop a transaction without fear of escalation?
Technology Helps, but Process Comes First
Voice-analysis and deepfake-detection technologies are improving, but no organization should make them its only line of defence.
Detection systems can generate false positives and false negatives. Synthetic media will continue improving. The more durable control is to make authenticity of a voice irrelevant to whether money can move.
That means combining strong identity controls, transaction monitoring, behavioural analytics, protected communication channels and enforceable approval workflows.
The Fideuram case should be viewed as a control-design warning.
Organizations have spent years building zero-trust principles for networks and identities. The same thinking now needs to reach executive instructions.
Do not automatically trust because the voice is familiar.
Verify the request, validate the beneficiary and preserve independent approval.
In the era of AI-generated identity, financial authorization must become deepfake-resistant by design.
To know more about Anand Shinde and his work in cybersecurity, awareness, and books:
https://anandshinde.com/
Have knowledge, experience, or a powerful idea you want to turn into a book? Get your book published with DevOM Publishing:
https://www.devompublishing.com/